
AWS cost · read-only scan
Your AWS bill is hiding money. I’ll show you where.
Connect your account read-only and see what it is wasting, in real dollars. The scan is free. The full report is $49-$149, set by your own bill.
15 of the 33 checks have no AWS equivalent.
- Interface VPC endpoints nothing calls
- Site-to-Site VPN connections with both tunnels down
- Log groups keeping everything forever
And 12 more. AWS finds the other 18.
AWS works from usage metrics, and these bill a flat rate used or not. This reads your account as it stands - nothing to switch on, no day of waiting.
- One CloudFormation button - no keys to paste, no agent to install
The role can only read - Get, Describe, List, nothing else. Read every permission it asks for before you connect, and delete the stack whenever you want. The scan adds about $0.10 to your own bill.
From nothing to a priced list in 90 seconds
Three steps, and you only do the first one. The times are what two strangers actually took, read off the server logs.
- 0:00
Launch one read-only role
A CloudFormation button opens in your own console. No keys to paste, no agent to install, and you can delete the stack whenever you like.
- 0:46
It reads every region you use
All 33 checks run across every enabled region, priced at that region's live rate - not a list price guessed from somewhere else.
- 1:25
You see the total before you pay
What it found per month, how many findings, and your price. Nothing is charged until you say so.
AWS’s own Compute Optimizer has to be switched on, then takes around 24 hours to analyse - and skips any resource less than 30 hours old.
The AWS way vs the AWSCost way
AWS gives you the tools free. None of them answers now.
The AWS way
- Day 0Switch on Compute Optimizer, and Cost Explorer for the prices.
- Day 0$29/month for Business Support+, for more checks.
- Day 1Up to 24h to analyse; a resource under 30h old is skipped.
- NeverVPC endpoints, EFS, snapshots, logs.
Free where it looks, blind to those four.
The AWSCost way
- 0:00Launch one read-only role.
- 0:46The role is live. The scan starts.
- 1:25The report is open - every finding, with its trade-off.
- 1:2533 checks. 15 that AWS never runs.
Ninety seconds, priced off your bill.
The role can only read - Get, Describe, List, nothing else. Read every permission it asks for before you connect, and delete the stack whenever you want. The scan adds about $0.10 to your own bill.
What one of these costs you, every month
These charges are flat. A NAT gateway that moved no bytes bills exactly what a busy one bills. Each figure is one typical resource at us-east-1 rates.
The chargePer monthDoes AWS find it
- OpenSearch domains nobody searches$407.34Nothing at AWS
- Aurora Serverless v2 minimum capacity$87.60Nothing at AWS
- Client VPN endpoints nobody connects to$73.00Nothing at AWS
- EKS clusters with no nodes$73.00Nothing at AWS
- Transit Gateway attachments carrying nothing$36.50Nothing at AWS
- Site-to-Site VPN connections with both tunnels down$36.50Nothing at AWS
- Fargate services nobody uses$36.04Compute Optimizer
- NAT gateways passing no traffic$32.85Compute Optimizer
- ElastiCache nodes with no connections$24.82Compute Optimizer
- Instances AWS sells cheaper today, same specs$24.09Compute Optimizer
- Interface VPC endpoints nothing calls$7.30Nothing at AWS
- Elastic IPs attached to nothing$3.65Trusted Advisor
- Public IPv4 addresses you pay for by the hour$3.65Nothing at AWS
The 6 most expensive things on that list have no AWS tool that looks for them. They publish no utilization, so there is nothing for Compute Optimizer to read - they just bill.
Every finding says what changing it costs
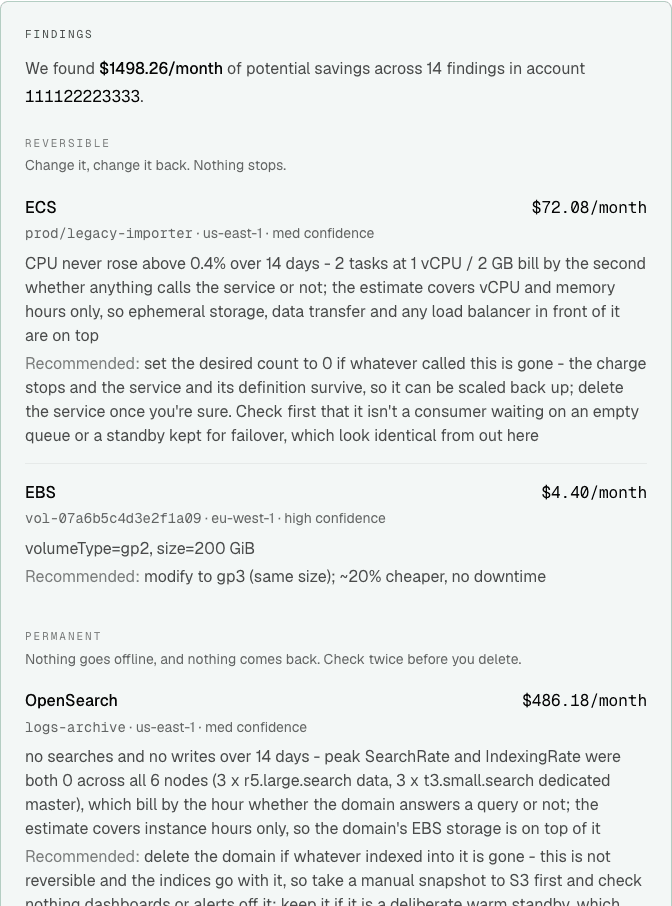
A list of savings is easy to write and dangerous to act on. Deleting a Transit Gateway attachment saves $36.50/month and severs every route through it. A cache that looks idle may be a warm standby somebody built on purpose, and it costs $24.82/month either way.
- Reversible
- Change it, change it back. Nothing stops.
- Permanent
- Nothing goes offline, and nothing comes back. Check twice before you delete.
- Interrupts something running
- The resource stops, restarts, or loses a path it had.
- A commitment you cannot cancel
- Nothing stops and nothing is deleted, but the term runs one to three years.
- Advisory
- Nothing to apply here - it shows you where the money goes.
And the limit of a read-only scan: it cannot prove a saving, because it never changes anything. Where it could not read something - a denied permission, a switched-off feature - the report names it rather than dropping it from the total.
Or do it yourself. Here is how.
Every check has an AWS CLI command behind it, and all 33 are written down on one page. Read-only, no sign-up, nothing to install beyond the CLI.
# Elastic IPs allocated but attached to nothing
aws ec2 describe-addresses \
  --query 'Addresses[?AssociationId==`null`].{IP:PublicIp,AllocId:AllocationId}' \
  --output table
Running the lot, once for every region you have switched on, is an afternoon. Doing it in 90 seconds is what you would be paying me for. All 33 commands →
Two strangers, start to finish
Both connected their own AWS account and read a report. Neither had spoken to me first. These times come off the server logs.
23 August 2026
85s
From signing in to reading the report.
The read-only role went live 46 seconds after they launched it. The scan then covered 17 regions.
1 September 2026
91s
From signing in to reading the report.
The read-only role went live 48 seconds after they launched it. The scan then covered 17 regions.
That is the connect step timed, and nothing more. What a scan finds depends entirely on what is in the account.
One payment, set by your own bill
Not a subscription and not a cut of what it finds - a read-only scan cannot prove a saving, so charging for one would be a promise nobody can keep.
$49
Under $2,000/month
$99
$2,000 - $10,000/month
$149
Over $10,000/month
You see what it found before you decide, and if the report is not useful, email within 14 days and I refund it. How the band is worked out →
Questions people ask first
What can the role actually do?
+
Read. Every permission it asks for is a Get, Describe or List, there is no write action anywhere in it, and they are all listed before you connect. Delete the stack and the access is gone.
Every permission it asks for →How long does it take?
+
About ninety seconds from signing in to reading the report. Two strangers connected their own accounts in 85 and 91 seconds, both across 17 regions. AWS's own Compute Optimizer has to be switched on first and then takes around 24 hours to analyse.
All 33 checks it runs →What does it cost?
+
One payment of $49, $99 or $149, banded off your measured AWS bill - not a percentage of what it finds, because a read-only scan cannot prove a saving. You see the total it found before you decide, and there is a 14-day refund.
How the band is worked out →What if it finds nothing?
+
Then you pay nothing. The scan and the total are free either way, and the price only appears once there is something behind it.
What a full report looks like →Can I just do this myself?
+
Yes, and the commands are published. Every one of the 33 checks has a read-only AWS CLI command written down. Running them all, once per region you have switched on, is an afternoon.
All 33 commands →See what your account is paying for.
The role can only read - Get, Describe, List, nothing else. Read every permission it asks for before you connect, and delete the stack whenever you want. The scan adds about $0.10 to your own bill.